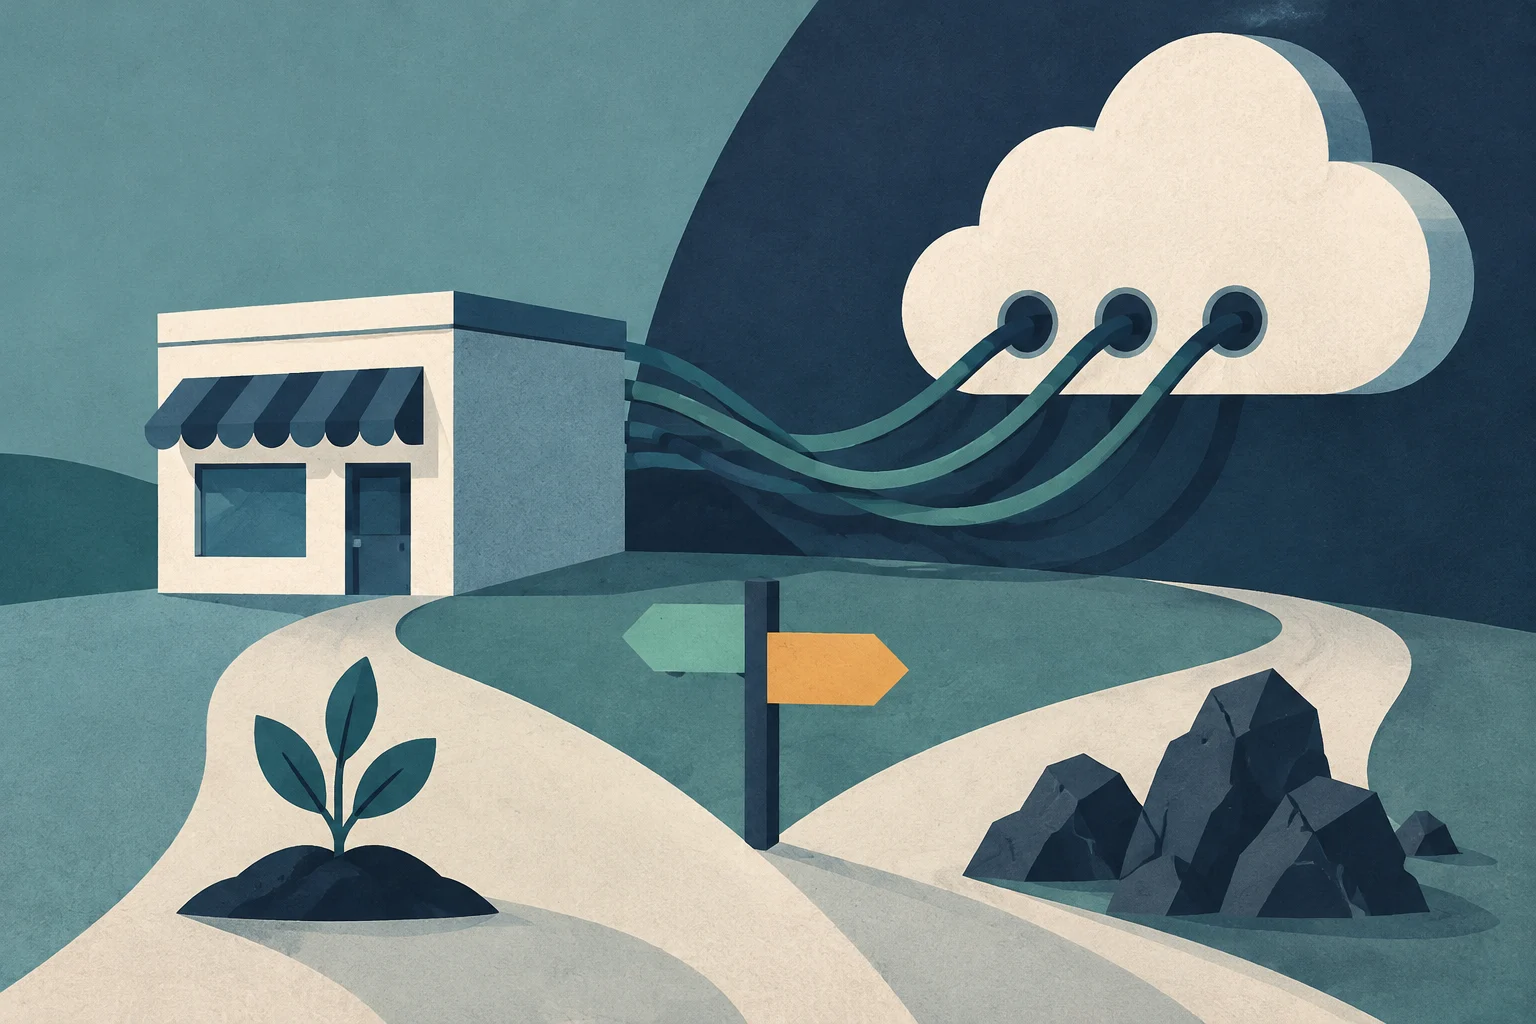
The integration of artificial intelligence in small and medium-sized enterprises (SMEs) has shifted from sporadic experimentation to a structural component of operations. However, this transition carries a strategic risk that is often underestimated: dependence on external providers. The phenomenon known as vendor lock-in not only limits technological autonomy but also introduces financial, operational, and regulatory vulnerabilities that can compromise business viability if not managed with an adequate digital sovereignty architecture.
The dual risk: superficiality and critical dependency
An analysis of AI risks in the Spanish business fabric reveals a paradox. On one hand, there is the risk of superficial AI, where companies use tools for isolated tasks (drafting, email summarization) without integrating them into measurable business processes. On the other hand, the risk of critical dependency emerges when AI is incorporated into essential flows such as sales, reporting, or customer service on third-party infrastructures that the company does not control.
According to Raúl Regalado Núñez, founder of R&R, the problem does not lie in using providers like OpenAI, Anthropic, or Microsoft, but in "building important processes as if those dependencies did not exist, did not cost anything, could not change, and did not affect data, margin, continuity, or management judgment". This lack of prior design of the dependency turns models, APIs, and clouds into single points of failure.
Types of dependency and operational vulnerabilities
To mitigate the risk, it is fundamental to distinguish between the two dimensions of lock-in:
- Technical dependency: Workflows, data, and integrations are built on proprietary APIs or non-portable formats. If the provider changes its interface or discontinues a service, migration requires a complete redesign of the processes.
- Commercial dependency: Contracts and terms of use are designed to make leaving difficult or to penalize it economically. SMEs, lacking negotiating power, are forced to accept fee increases or changes in usage limits with little prior notice.
This exposure is aggravated by the lack of governance. Recent data indicates that only 6% of organizations have governance frameworks ready to supervise autonomous AI agents, while 75% of employees already use AI tools without formal company authorization (shadow AI). This disconnect between actual use and corporate supervision increases the probability of security incidents and data leaks.
Regulatory and financial impact in the EU
The European regulatory context adds an additional layer of complexity. The Regulation (EU) 2024/1689 (AI Act) introduces tiered obligations for human supervision, traceability, and documentation. Fines for non-compliance can reach 35 million euros or 7% of global turnover.
For SMEs, the risk is not only legal but also financial. IBM estimates that shadow AI adds an average of 670,000 USD to the cost of a data breach. Furthermore, the interruption of service by a single provider can paralyze operations. In Spain, organizations supported an average of 1,968 cyberattacks weekly in 2025, a 70% increase compared to 2023, according to Check Point Research, an environment where the lack of resilience in AI architectures becomes an exploitable attack vector.
'Managed dependency' strategies
The response to these risks is not total sovereignty (developing proprietary models), which is rarely viable for an SME, but managed dependency. This strategy involves designing the relationship with the provider to maintain the ability to exit and operational continuity.
Modular architecture and diversification
Building on modular architectures allows decoupling business logic from the specific provider. This implies:
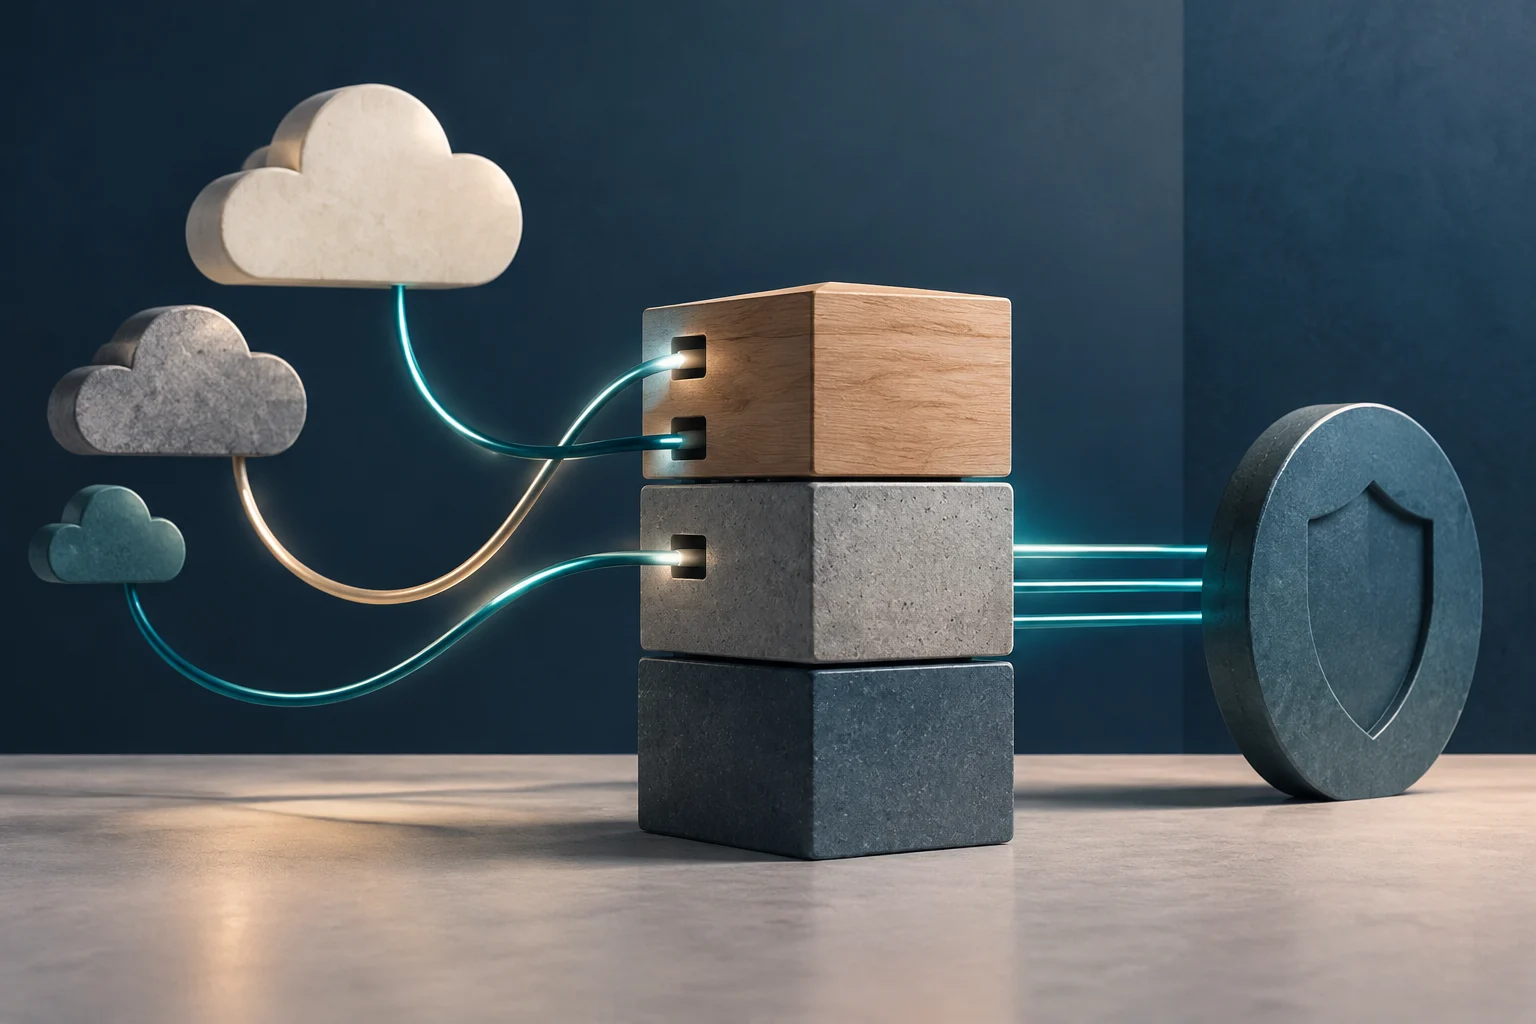
- Provider diversification: Avoiding a single provider controlling the complete lifecycle of a critical process.
- Portable formats: Establishing data standards that allow migration between platforms without loss of information.
- Abstraction layers: Using intermediaries or software layers that allow changing the underlying AI model without rewriting the entire application.
Human supervision and governance
Implementing a three-layer model (read, propose, execute) allows limiting the risk. In this model, the AI agent can read data and propose actions, but the execution of critical actions requires human approval. This not only mitigates the risk of algorithmic errors but also complies with the human supervision obligations of the AI Act.
Conclusion
The adoption of AI in SMEs must evolve from a reactive approach to a strategic one. The risk is not the technology itself, but the lack of design of the dependency it generates. By implementing modular architectures, diversifying providers, and establishing clear governance frameworks, companies can leverage the benefits of AI without compromising their operational continuity, financial margin, or regulatory compliance in the European Union.